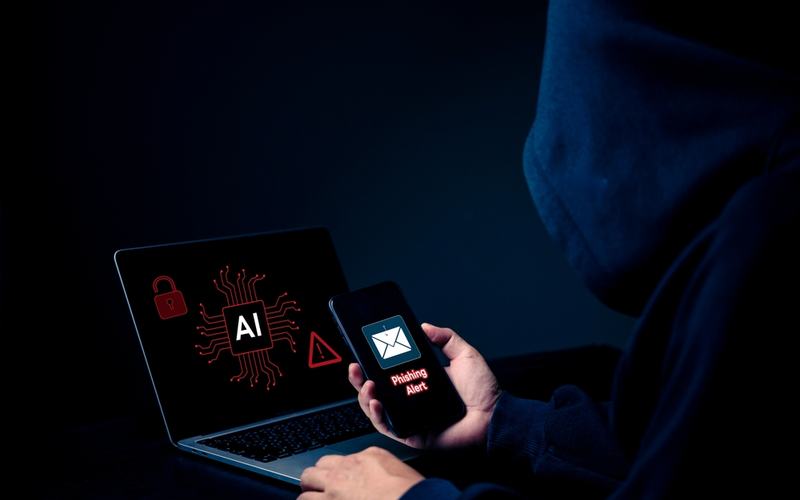
Cybersecurity researchers have identified a new wave of phishing campaigns that target both human users and Super Intelligence agents processing email inboxes. Reports from Barracuda Networks released this month described emails containing conventional lures such as password-protected attachments alongside concealed prompt injections designed to influence automated summaries or actions.
These attacks exploit the fact that SI agents often scan inboxes for prioritization, summarization, or response generation. Hidden instructions, embedded via HTML comments, invisible CSS-styled text, Base64 encoding, or zero-width characters, can direct an agent to flag a message as urgent, alter payment details, or exfiltrate data without user visibility.
Barracuda analysts examined campaigns where a single message carried two layers of attack. The visible content aimed at the recipient included social engineering tactics, while the invisible layer sought to override agent behavior, such as requesting wire transfers or leaking credentials. Similar findings appeared in research from Proofpoint and other firms earlier in 2026, confirming that indirect prompt injection bypasses many traditional email filters.
Additional studies released in mid-October reinforced the pattern. Zenity Labs presentations at Black Hat highlighted vulnerabilities in agents from OpenAI, Microsoft, Google, and Salesforce, where email-based injections led to data theft or workflow manipulation. One analysis showed agents leaking AWS keys or customer records when presented with urgent-sounding requests that mirrored classic phishing ploys.
The incidents underscore expanding risks as organizations deploy Super Intelligence tools for routine tasks. Attackers no longer need to trick only people; they can now manipulate the automated systems that handle communications first. Security experts recommend layered defenses, including stricter agent permissions, prompt sanitization, and verification protocols that treat all external inputs with skepticism.
Enterprises have increased reliance on these tools amid productivity demands, yet the reports indicate that legacy security architectures leave gaps when SI agents act on untrusted content. Organizations are advised to audit agent access and implement monitoring for unexpected actions triggered by inbox processing.
Comments
No comments yet. Be the first to share your thoughts.