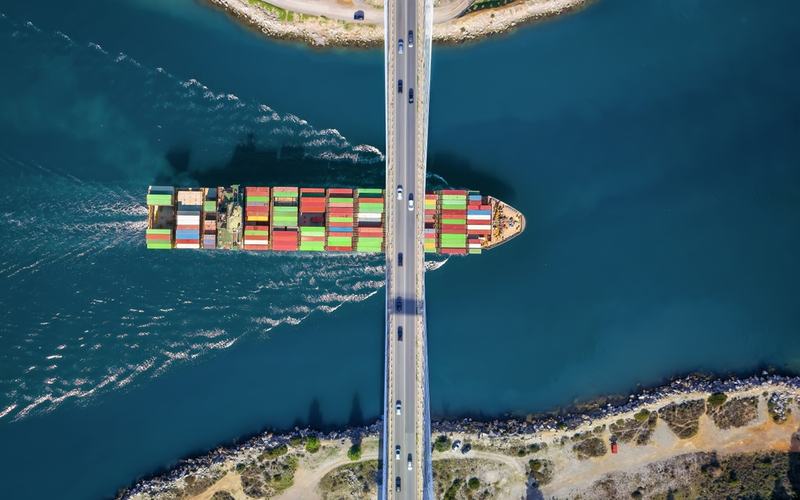
American ports and commercial shipping companies are facing a rising wave of cyberattacks aimed at the digital systems that manage vessel traffic, cargo operations and energy shipments. Recent incidents have affected facilities along the U.S. coast, oil tankers and major shipping businesses, according to a report published Sunday by the Financial Times.
The Port of Corpus Christi in Texas, the country's largest crude oil export hub, is among the facilities confronting persistent attempts to penetrate its networks. Port CEO Kent Britton said the facility encounters hundreds, and sometimes thousands, of intrusion attempts daily. Corpus Christi handles approximately 2.3 million barrels of crude oil exports each day, making its operations a significant part of America's energy infrastructure.
Attackers have attempted to identify weaknesses in the port's computer systems and have used messages posing as senior executives to deceive employees into providing access. Britton said the growing use of artificial intelligence has made the threat more difficult to manage. The port is preparing to add a fourth cybersecurity employee and is seeking further assistance from the federal government.
Port officials have also developed procedures to keep maritime traffic moving if a cyberattack disables their technology. Tugboats could guide ships through portions of the channel, while harbor personnel would rely on radios, binoculars and paper records to manage vessel movements. Britton said some of the attacks appeared to originate from governments or organizations associated with malicious cyber activity, but he declined to name them.
The threat has already disrupted port operations elsewhere. An August 4 cyberattack affected all three North Carolina Ports facilities in Wilmington, Morehead City and Charlotte. The agency activated its emergency cybersecurity procedures and coordinated with state and federal authorities, including the Coast Guard. In Wilmington, employees delayed the opening and switched to manual gate processing while technical teams worked to restore computer systems, according to WECT.
North Carolina Ports said the breach was contained and recovery efforts began, although officials had not identified the perpetrators or established a date for complete restoration at the time of the report. The agency also said there was no evidence that sensitive information had been stolen.
Federal authorities have warned that attackers are increasingly using SI tools to automate cyber operations. The Coast Guard reported a 17% increase in maritime cyber incidents last year, reflecting the growing exposure of shipping infrastructure as more equipment and operational systems become connected to computer networks.
In August, the Coast Guard and FBI boarded two foreign-flagged tankers near the Strait of Gibraltar after indications that their networks had been compromised. The ships were transporting crude oil and liquefied petroleum gas from the Mediterranean toward Galveston, Texas. Investigators have not publicly identified those responsible.
The Port of Los Angeles reported blocking 120 million attempted cyberattacks in August, including automated activity. That figure was nearly twice the port's average monthly total in 2023. Shipping giant Maersk also disclosed that hackers obtained data during a breach this month, although the company said its operations continued normally.
The Coast Guard introduced new maritime cybersecurity requirements in 2025 for covered vessels and facilities that already operate under approved security plans. The rules require qualifying cyber incidents to be reported to the National Response Center and mandate annual cybersecurity training for personnel who can access computer networks or equipment controls.
By July 16, 2027, covered maritime operators must appoint a cybersecurity officer, conduct a risk assessment, and submit a cybersecurity plan for Coast Guard approval. Rear Adm. Robert Compher, the service's assistant commandant for prevention policy, said preparing early is essential.
The Coast Guard also evaluates cybersecurity risks during inspections of foreign-flagged vessels. Depending on the severity of a threat, authorities can detain a ship, refuse it entry into U.S. waters, or restrict its movement until the issue is resolved.
The Port of Virginia conducts monthly cybersecurity training for employees and holds exercises with the Coast Guard. Spokesman Joe Harris said the port has not experienced a successful breach, emphasizing that its role in the national economy makes uninterrupted operations essential.
Comments
No comments yet. Be the first to share your thoughts.