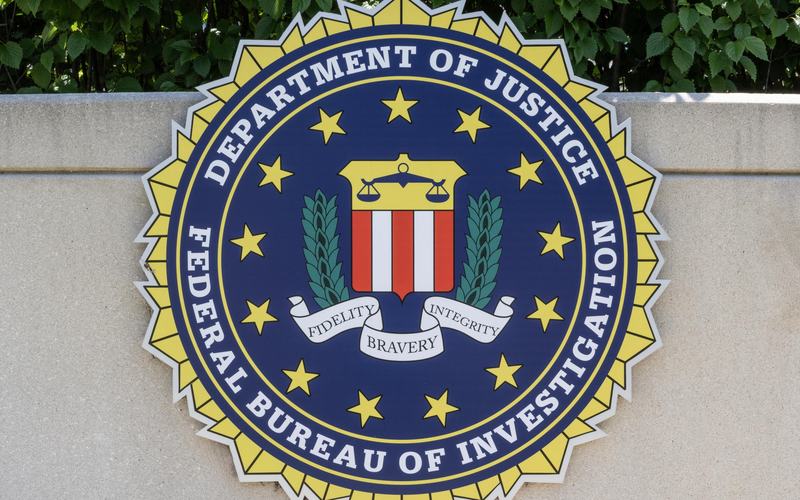
The FBI and Department of Justice announced Thursday that they had seized two cyberattack tools used by hackers linked to the Chinese government, disrupting operations targeting critical infrastructure, universities, airports, and other organizations in the United States and abroad.
The tools, known as “Microscan” and “FishHub,” were associated with a hacking campaign tracked by cybersecurity researchers as Flax Typhoon. Federal investigators have identified China-based information security company Integrity Technology Group as the organization behind the operation, alleging that the company has contracts with the Chinese government.
According to the FBI, Microscan was used to identify and target vulnerable systems, including those belonging to an unnamed American power company, airports in Japan and Poland, Taiwanese universities, a multinational nongovernmental organization, and critical infrastructure companies in Taiwan.
FishHub supported phishing attacks that enabled hackers to gain remote access to victims’ computer networks. Phishing typically involves deceptive emails or messages designed to trick recipients into revealing sensitive information or opening a pathway into protected systems.
Federal officials said the seizure rendered both tools inoperable, disrupting capabilities used in the broader hacking campaign. The operation reflects a law enforcement strategy focused on dismantling the infrastructure and resources that cybercriminal groups and state-linked actors rely on to conduct attacks.
“We aim to remove the capability from the threat actors. We target their infrastructure, their money, and their tools,” said Jason Bilnoski, deputy assistant director of the FBI’s Cyber Division. He described the hacking activity as “indiscriminate and reckless.”
The latest action builds on an earlier FBI operation against Flax Typhoon. In September 2024, the bureau announced that it had disrupted a network of more than 200,000 compromised consumer devices, including internet-connected cameras, digital video recorders, and home and office routers.
Those infected devices had been assembled into a botnet, a network of compromised computers and other internet-connected equipment that can be controlled remotely. Such networks can be used to conceal malicious activity, facilitate cybercrime, and provide access to victims’ systems and sensitive information.
The earlier disruption targeted the infrastructure supporting the hacking campaign, while Thursday’s seizure focused on tools used to identify vulnerable systems and gain access to networks.
Federal investigators say the operation is part of a continuing effort to prevent the group from rebuilding its capabilities. Brett Lally, an FBI supervisory special agent in San Diego, said the bureau would continue monitoring for signs that Integrity Technology Group might reconstruct the infrastructure used in its cyber operations.
The case highlights ongoing concerns about cyber operations attributed to Chinese-linked actors, particularly attacks involving critical infrastructure and organizations whose systems support essential services. Disrupting the tools used in those campaigns can limit attackers’ ability to reach new targets, although authorities will continue watching for attempts to restore the network and resume operations.
Comments
No comments yet. Be the first to share your thoughts.