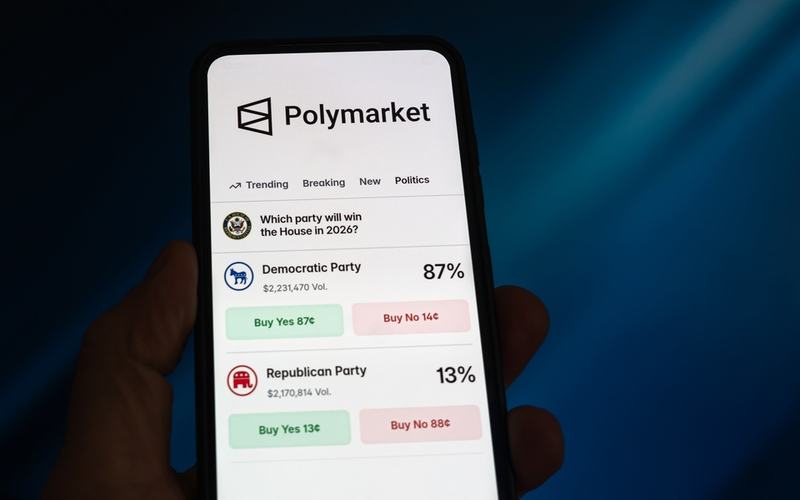
Polymarket users reportedly lost approximately $2.6 million Thursday after malicious code was delivered through the prediction market’s official website, allowing an attacker to liquidate trading positions and transfer funds out of affected accounts.
The incident was first reported at approximately 1:30 p.m. Eastern time, when users began complaining that their cryptocurrency wallets had been drained and their open positions sold without authorization. The total number of affected users has not been established.
People monitoring the incident said the breach involved malicious code delivered through DebugBear, a third-party analytics provider whose software was embedded on Polymarket’s website. The code reportedly gathered information from active users and exploited trading credentials stored in their browsers’ local storage.
According to one user who described the attack, the malicious script systematically sold open positions, initially at prices slightly below market value before making progressively deeper discounts to liquidate the remaining holdings. The attacker then reportedly converted the proceeds into Polygon’s POL token or USD Coin, a cryptocurrency designed to track the U.S. dollar, before transferring the funds to an attacker-controlled address.
The malicious code was reportedly removed at approximately 2 p.m. Eastern time, when Polymarket suspended trading as it worked to address the security issue.
A company employee confirmed that the platform had identified and fixed a problem affecting its international website, Polymarket.com. The employee said a third-party provider had been compromised and that the incident had been referred to law enforcement.
“Anyone who has been impacted will be made whole,” the company said, promising to reimburse affected users.
Blockchain transaction records placed the reported losses at approximately $2.6 million, although the full scope of the incident and the number of victims remained unclear. Trading resumed at 3 p.m. Eastern time Thursday.
DebugBear, a United Kingdom-based analytics company, acknowledged the ongoing security incident and urged customers using its real-user monitoring product to remove the embedded code from their websites.
The incident highlights the security risks posed by third-party software integrated into cryptocurrency trading platforms. Even when a platform’s core infrastructure is not directly breached, compromised external services can potentially expose users to malicious code capable of exploiting browser-stored credentials and authorizing unauthorized transactions.
Polymarket has not publicly identified the attacker or disclosed a final accounting of the losses. The investigation is ongoing.
Comments
No comments yet. Be the first to share your thoughts.